NR-04 · Deimos AI LLC · California, USA · 2026-10-21
Fully updated Macs still trust the leaked eMudhra keys in git, curl, python3 and openssl, Deimos AI LLC finds.
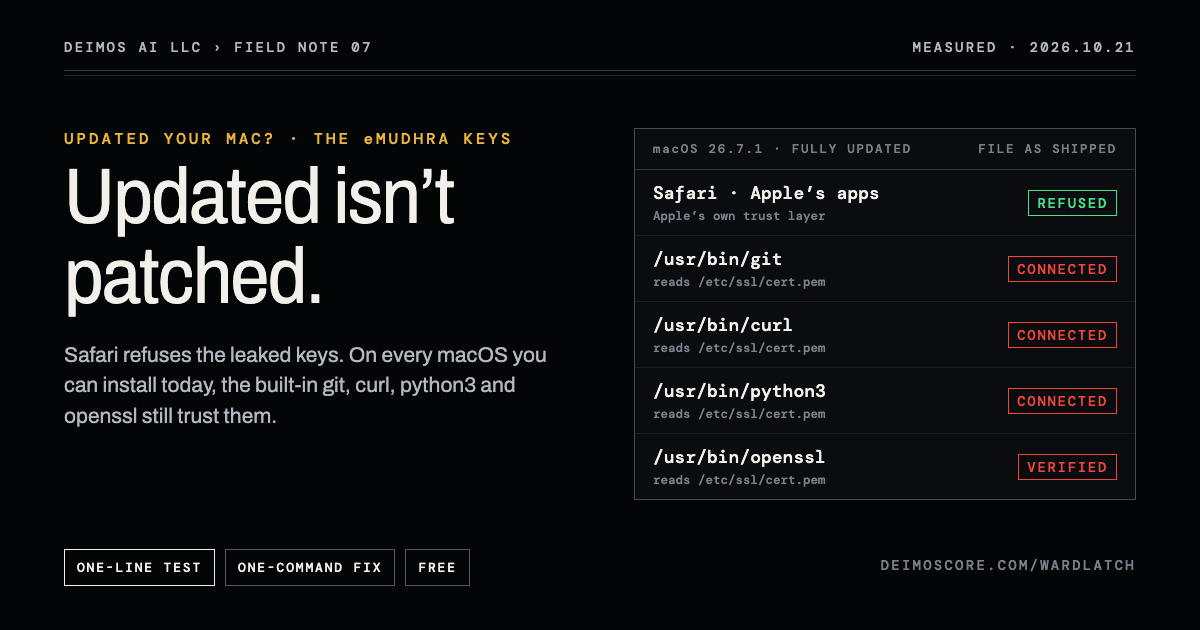
Safari is protected. On every macOS release available today, the Mac’s built-in git, curl, python3 and openssl still trust the leaked eMudhra keys.
On 21 October 2026 Deimos AI LLC measured what a fully updated Mac trusts after the eMudhra compromise, in which the private keys of 8 intermediate certificate authorities turned out to be recoverable by anyone. Safari and Apple’s apps refuse sites signed with those keys. The Mac’s built-in command-line tools do not.
On macOS 26.7.1 with every update installed, 4 built-in tools, git, curl, python3 and openssl, accepted a test site signed with a compromised key. They check certificates against /etc/ssl/cert.pem, a file that changes only with a new version of macOS. All 3 current releases, macOS 27.0.1, 26.7.1 and 15.8.1, came out on 28 September, before the keys were reported on 17 October, so installing every update leaves the file as it was.
Why git matters
The incident’s advisory already warns that the Mac’s curl reads this file, and publishes a fix. The measurement shows the same file serves git, the tool developers use to fetch code. Anyone holding one of the leaked keys and sitting in a Mac’s network path, on public Wi-Fi, a compromised router or a hijacked DNS server, could serve a forged repository to git clone, a forged install script to a curl … | sh one-liner or a forged download to a Python script, and the tools would accept it. Nothing leaks from the Mac itself; it is open to impersonation.
Test and fix in a minute
The Wardlatch page gives a one-line test to paste into Terminal, which prints EXPOSED, SAFE or UNKNOWN, and the advisory’s one-command fix, which backs the file up first and asks for the Mac’s password. One answer covers all four tools. Field Note 07 sets out the measurement, including the control that rules out a network failure.
Deimos AI LLC has asked the advisory’s maintainers to name git, python3 and openssl in its macOS section (issue 45 on GitHub).
For businesses
Every Mac a team develops or builds on is in this state until the file is fixed. Deimos AI LLC recommends pushing the fix through device management, or treating those Macs as exposed on any network the business does not control, until Apple ships a macOS release that replaces the file. Wardlatch, free and open source, checks the rest of the machine with npx wardlatch.
Share this release
The facts in this item · from the Record
Each number is pinned as it stood when this item was published, 2026-10-21. The Record keeps the live value; if it moves, the row says so and this item’s text is not rewritten.
- 8eMudhra intermediate CA keys found compromised (6 for websites, 2 for code signing)Check it: eMudhra intermediate CA keys found compromised (6 for websites, 2 for code signing), on the Record
- 4Built-in macOS command-line tools that accepted a site signed with a leaked eMudhra key on a fully updated Mac (git, curl, python3, openssl; macOS 26.7.1, /etc/ssl/cert.pem as shipped)Check it: Built-in macOS command-line tools that accepted a site signed with a leaked eMudhra key on a fully updated Mac (git, curl, python3, openssl; macOS 26.7.1, /etc/ssl/cert.pem as shipped), on the Record
- 3Current macOS releases (27.0.1, 26.7.1, 15.8.1), all dated 28 Sep 2026, before the eMudhra keys were reported on 17 OctCheck it: Current macOS releases (27.0.1, 26.7.1, 15.8.1), all dated 28 Sep 2026, before the eMudhra keys were reported on 17 Oct, on the Record
Sources
Image pack
About Deimos AI LLC
Deimos AI LLC builds software that keeps people in charge of their AI agents: seen, approved, stoppable and provable. Its instruments include Ratchet, a live effect gate; Crimp, an open-source decision gate; Marklode, startup due diligence checked by a person; and Clockford™, whose private beta opens Nov 10th, 2026. It publishes a dated, sourced ledger of its claims. Defence only.
Media contact
No press inbox is published yet, and this site has no forms. Message Deimos AI LLC on LinkedIn, or use the contact page.